After Black October: Is manufacturing prepared for the next disruption?
October 2026 brought a series of major cybersecurity incidents, leading some to describe the period as 'Black October'. While the attacks were not part of a single coordinated event, they've exposed weaknesses in the digital systems that businesses all over the world rely on [1]. The consequences can extend beyond IT systems, affecting production, equipment and essential supplies.
Research from Make UK found that 30% of UK manufacturers experienced a cyber incident in the previous year, either directly or through their supply chain. Yet only around half had incident-response plans in place [2]. These findings highlight the need for manufacturers to prepare for disruption across both their digital systems and physical supply chains.
How cyberattacks are disrupting supply chains
In October, cyberattacks affected refrigeration systems at approximately 700 French supermarkets, causing equipment failures and food losses. Some affected systems used older controllers that no longer received security updates [3].
Further apparent attacks were reported on 2 November in Sweden, Belgium, Luxembourg and Estonia, although no confirmed connection between the incidents had been established [4]. While these attacks targeted retail refrigeration, they demonstrate how compromised control systems can cause physical disruption.
Manufacturers face similar risks through their suppliers. In August 2026, medical technology manufacturer Boston Scientific experienced a cyber incident that disrupted manufacturing, order processing and distribution, leading to delivery interruptions [5].
Make UK's research found that 31% of manufacturers affected by supplier cyberattacks experienced delays to customer deliveries [2].
These incidents add to existing supply chain pressures. Aviva's October 2026 research found that 84% of surveyed small and mid-sized UK manufacturing and industrial businesses experienced unplanned downtime at least monthly. Supply chain disruption was the leading reported cause (22%), followed by cyber incidents (17%) [6].
With production dependent on connected equipment and external suppliers, manufacturers need recovery plans that account for both cybersecurity and component availability.

Five steps to improve manufacturing resilience
The UK's National Cyber Security Centre (NCSC) recommends identifying critical systems, assessing supplier dependencies and testing recovery procedures [7].
Manufacturers can strengthen their preparations by focusing on five areas.
1. Identify critical production equipment
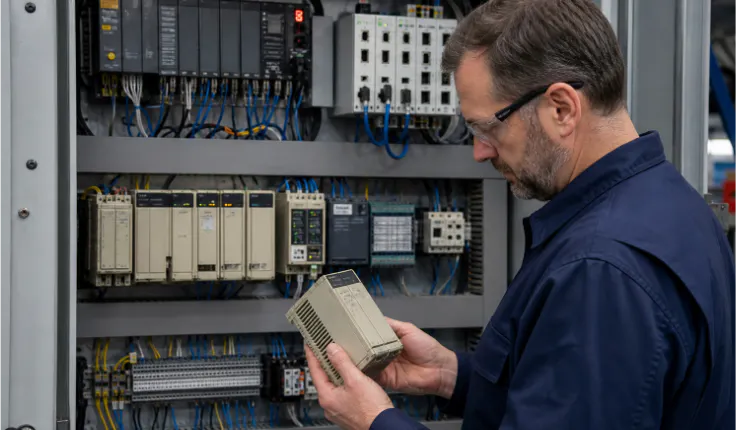
Maintain an accurate record of essential machinery, industrial networks, programmable logic controllers (PLCs), drives and human-machine interfaces (HMIs).
Prioritise equipment according to its importance to production, the consequences of failure and the time needed for recovery.
2. Review supplier dependencies
Identify suppliers responsible for critical components and establish alternative sourcing arrangements where possible.
Keep essential part numbers, specifications and supplier contacts accessible in case normal purchasing systems become unavailable.
Our guide to managing automation components in a disrupted supply chain explores ways to reduce sourcing risks.
3. Check spare parts availability
Equipment failures during recovery can extend downtime, particularly when replacement components are obsolete or difficult to source.
Review spare parts inventories, lead times and compatibility requirements. Prioritise components whose failure would have the greatest impact on production.
Effective strategic spare parts planning can help manufacturers balance stockholding costs against downtime risks.
4. Assess ageing automation systems
Older industrial control systems may no longer receive manufacturer security updates, increasing potential risks when connected to wider networks.
Review equipment support status and work with qualified specialists to assess security measures, including network access controls and planned upgrades.
Consider how obsolete automation components affect maintenance and replacement planning.
5. Test recovery procedures
Business continuity plans should account for several problems occurring simultaneously.
Test scenarios involving unavailable purchasing systems, supplier outages and equipment failures. Confirm responsibilities, alternative communication methods and procedures for safely restarting production.
Keeping critical components available
Cybersecurity measures are essential, but manufacturers must also prepare for equipment failures and supply interruptions.
EU Automation sources new, reconditioned and obsolete automation components from more than 100 manufacturers, helping businesses find parts that may be difficult to obtain through traditional purchasing channels.
Through its global supplier network, EU Automation supports maintenance and procurement teams sourcing critical PLCs, drives, HMIs and other industrial control equipment.
While replacement components cannot resolve a cyberattack, reliable sourcing arrangements can help prevent parts shortages from extending operational downtime.
Preparing for future disruption
Black October has highlighted the risks facing manufacturers that depend on connected systems and complex supply chains. With clear recovery plans and regular testing, manufacturers can reduce downtime and maintain production continuity when unexpected challenges arise.
Identifying critical equipment, reviewing supplier arrangements, and maintaining access to essential components can help businesses respond more effectively when disruption occurs.
References
[1] Progressive Policy Institute (2026). Cybersecurity's "Black October". 29 October 2026.
[2] Make UK (2026). Cyber Security in Manufacturing. 10 August 2026.